Five ways in for AI applications and automations, from due diligence to running them, each with an agreed scope, a written acceptance test and a named person accountable for the work. For consulting firms and integrators delivering under their own name, and for teams with AI work to take further.
Start from where your AI work is today, or check the code before you commit. Each package is priced, scoped and accepted the same way, and you can stop after any of them.
IdeaPilotLiveOwned
IdeaLive
One defined automation
One specific workflow delivered end to end. AI agents take on tasks one at a time, under set authority, with a named person accountable for every action.
Accepted when The workflow runs on agreed cases with agreed results, and every agent action is logged.
A pilot that demoed well, rebuilt to run for real: a locked scope, tests and evaluations, a security review, and deployment to the environment you choose.
Accepted when It passes the acceptance test written with you before the start: what must run, on which data, with which result.
After go-live we keep it running and improving under an agreed support arrangement, or hand over the code, the documentation and people ready to own it.
Accepted when Service levels, or the handover checklist, are agreed at the start, not at the end.
Before you buy, fund, take over or fix it: the code, the architecture, security, open-source licences and who really holds the knowledge, evidenced and costed. An Express Audit of a live AI application takes about a week; full technical due diligence takes ten business days from access.
Accepted when The agreed reports and the readout are delivered. Never a minimum number of findings, and never a promise that nothing is wrong.
What is in and what is out, in writing, before anyone builds.
Acceptance test
What must run, on which data, with which result, and who signs it off.
Build in packages
Agents work under set authority; a person reviews what they produce.
Stop point
After each package: continue, change course, or stop.
We answer for the agreed scope and its acceptance test. A prototype shows an idea works on a few cases; production needs tests, evaluations, security, monitoring and an owner. We say which one you are getting before we start.
Due diligence before you commit.
Buying a software company, funding one, taking over an application or about to fix one? Find out what the code really is first: evidenced, confirmed by a qualified reviewer and costed to fix.
Express Audit
For an AI application that is already live. It is also the usual first step of Stabilise.
Time
About one week
Fee
From US$2,500, fixed
Checked against OWASP ASVS and the OWASP Top 10 for LLM applications
A risk register, ranked by severity
A remediation plan with a cost estimate, before you commit to the fix
A free re-quote if the findings change the size of the fix by more than 20%
Technical due diligence
For a platform you are buying, funding or taking over. From access to readout it runs alongside the wider deal work, so both land together.
Time
Ten business days
Fee
Fixed, agreed to the scope
Two kinds of evidence: an engineering benchmark built on research from Stanford University, placing the team against industry peers by sector and company size, and a deep audit of the source code
Technical debt costed in person-days, with a prioritised remediation roadmap
Key-person dependency: who holds which parts of the code, and what is exposed if they leave
A software bill of materials, with open-source licence and vulnerability risk
On request, a specialist review of the AI model itself: training data, approach, validation, performance and reproducibility
What we check
Architecture
System design and boundaries, how modules and services fit together, data and integration flows, and drift from the intended design.
Code quality
Complexity, duplication, coupling and test coverage, with technical debt costed in person-days rather than described.
Security
Application security, secrets, infrastructure, containers and pipelines, reviewed against OWASP ASVS and mapped to CWE and OWASP references.
Open source and IP
Every direct and transitive dependency, known vulnerabilities, licence classification and copyleft exposure in the product.
People and ownership
Who holds which parts of the code, the bus factor per module, code written by people who have left, and the contractor and in-house split.
Testing and DevOps
Test strategy and gaps, build reproducibility, pipelines and releases, and readiness to run in production.
The code stays where its owner wants it.
The owner chooses where it runsInside their own VPN, virtual desktop or private cloud, a workspace they control, or an isolated environment of ours.
Read-only and revocableAccess is read-only, limited to named people, logged, and can be withdrawn at any time.
Nothing leaves without approvalNo code goes to an outside service without written approval. It can run with no external AI model at all.
Deletion, confirmed in writingCopies and working files are deleted at close-out. Our delivery partners hold ISO 27001 and SOC 2 Type II.
Every finding is confirmed by a qualified reviewer before it reaches the report; AI does not set the final severity. An assessment is not a penetration test or a legal opinion on licences, and both can be scoped separately.
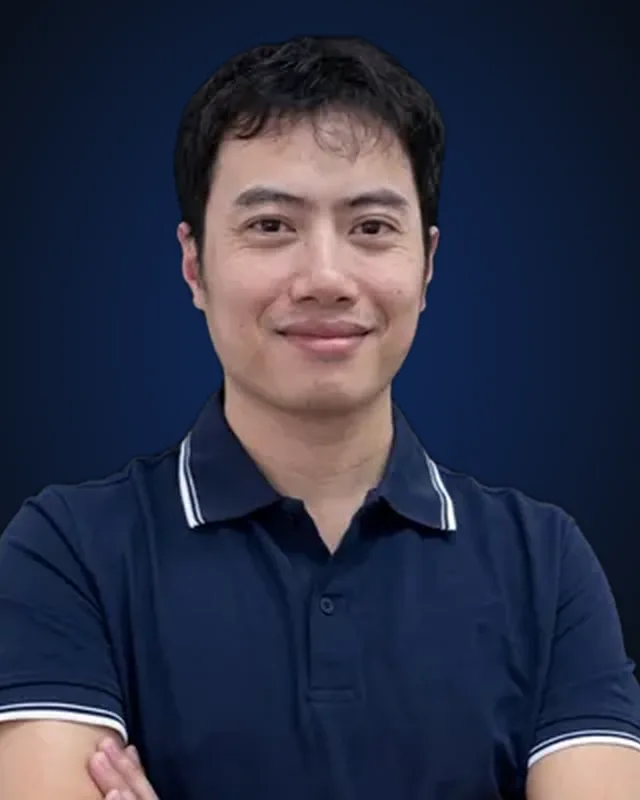
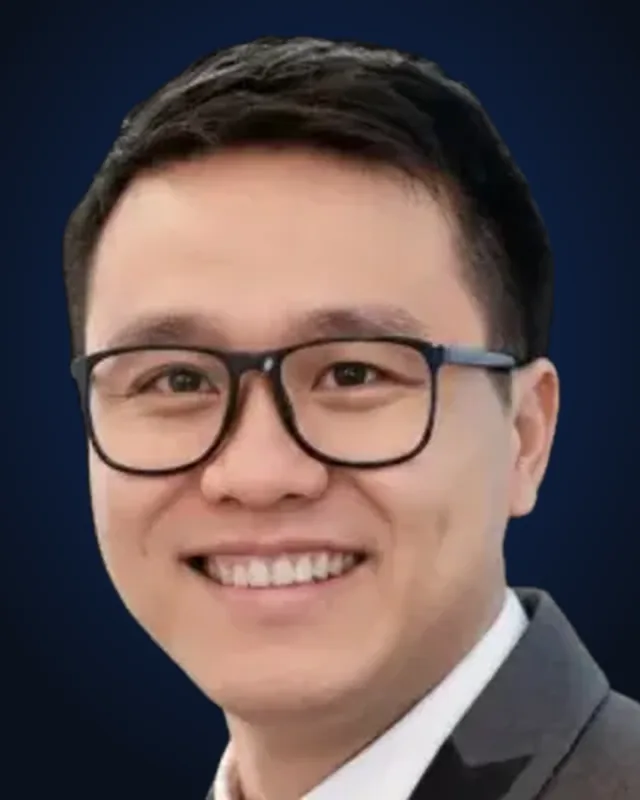
Senior engineering leaders at the Vietnam delivery partners we work with. They own architecture, agentic engineering practice and the review gates on AI-generated code.
Ha Bui
Delivery Lead
18+ years as CTO, Director and Founder. Leads a Vietnam-based delivery firm trusted by Fortune Global 500 companies, shipping enterprise-grade systems across 15+ countries.
Do Tien Thanh
Chief Technology Officer
Runs engineering around a structured 9-stage delivery process (planning, four-layer testing and a signed closure report on every project), built over years of shipping software for international clients.
Senior architect leading agentic engineering delivery: system design, spec-driven build, and review gates on AI-generated code.
Tuan Nguyen
CTO and Co-Founder
RWTH Aachen graduate based in Germany. Co-founded and leads engineering at a Vietnam-based delivery firm, bridging European client relationships with Vietnam delivery for Fortune Global 500 companies.
Delivered before, by our network.
299 projects in our library match this kind of work. Three examples, anonymised:
Generative & agentic AI
From Manual Support to Intelligent Automation: An AI Agent Transformation in Fintech
Fintech & payments, Switzerland
OpenAI / GPT
LangChain
LangGraph
React
Generative & agentic AI
Boosting HR Productivity with AI-Powered Recruitment Software
Professional services, Vietnam
OpenAI / GPT
Python
MongoDB
React
Generative & agentic AI
AI Motor Insurance Automation (A Leading Vietnamese Motor Insurer)
Every package is written down the same way before anyone starts. An illustration, not a client project:
Example: a document-processing pilot taken to production
Scope
Rebuild a working pilot as an application your client can run: two document types and one integration.
Price
Fixed, agreed before the start. A change becomes a new package, not an overrun.
Acceptance test
Written with you before work starts: which documents, which fields, what accuracy on an agreed test set, and what a person reviews.
Agents
Used task by task under set authority. Every agent action is logged, and a person reviews the output.
On your side
One named owner who accepts the work and keeps the client conversation.
On our side
A named lead, the engineers the package needs, the evaluations and the delivery record.
After it
A stop point. Run it with us, hand it over, or stop.
The questions partners ask first.
Straight answers. Ask us anything else on a call.
Do you guarantee the result?
We commit to the agreed scope and its acceptance test, in writing. What the application does for the business afterwards also depends on how it is adopted and used, so we do not promise outcomes beyond the scope.
Can you take over an application someone else built?
Yes. A stabilise engagement starts with a fixed-price review of the code, the infrastructure and any evaluations, before a single fix is priced.
How are AI agents used in delivery?
Task by task, under set authority. Each agent has a defined job and a named person accountable for what it does, and its output is reviewed before it is accepted. The level of autonomy is agreed per task, not assumed.
Does the code leave the owner's environment during due diligence?
No, unless the owner approves it in writing. The assessment can run inside their own VPN, virtual desktop or private cloud, access is read-only and can be withdrawn at any time, and copies are deleted at close-out with written confirmation.
Is a code assessment a penetration test or a legal review?
Neither. It reviews the source code, architecture, dependencies and how the team works. Penetration testing, a cloud configuration audit and a legal opinion on licences or IP can be scoped separately.
Who signs with the client?
You do, when you are the prime. We contract with your firm, and your client sees your firm throughout.
Do we work with Nessoris or with vitX?
With Nessoris when you want an agreed scope delivered, and run if you choose. If you need named engineers inside your own team, directed by you, that is our sister company vitX.
If you accept, HubSpot sets cookies for analytics, our chat and the booking calendar. If you reject, the site works the same without them. You can change this any time under Cookie settings.